Microsoft has introduced security changes that could affect workflows using the Resilient File System (ReFS) on certain removable or externally attached storage. Organizations with these configurations have until January 2027 to assess dependencies, move workloads to supported storage, and validate the changes.
What's changing with ReFS on external storage
ReFS, or Resilient File System, is a Microsoft file system designed to support data integrity, resilience, and large storage workloads. Applications and operational processes can depend on data held on a ReFS volume. Blocking that volume from mounting makes its data unavailable through that connection and can interrupt the processes that use it.
Windows updates released on or after October 13, 2026, enable default auditing for unsupported ReFS configurations on qualifying external media. The January 2027 security update will enable blocking by default unless an administrator explicitly changes the applicable setting. Microsoft’s guidance explains the affected configurations and the steps administrators should take.
Scaling your response to the audit findings
The scope of the response should follow the findings. An organization may identify a small number of volumes that a storage team can address through its existing change process. More complex dependencies may require coordination across infrastructure, application teams, and business owners. The assessment establishes which approach is appropriate.
In either case, the work follows a familiar sequence: identify the dependency, assign an owner, agree on remediation, and validate the result. Recording those decisions gives the organization a clear view of what remains open and who is responsible for completing it.
Five practical next steps
1. Establish your exposure
Review the relevant ReFS audit findings and identify affected configurations. Include storage connected intermittently, and allow an observation period that covers the operational processes under assessment. Record the systems and usage patterns covered so the conclusions have a clear basis.
2. Assign ownership and assess the impact
Identify what depends on each affected volume and who can approve and execute the required changes. Establish the consequences of losing access, including any dependencies on scheduled or occasional processes. Use that information to determine priority and the level of coordination needed.
3. Agree on a dated remediation plan
Define the supported storage configuration, migration approach, and completion date. Leave time for validation and rework before January’s update reaches the affected systems. Where a temporary override is required, document its approval, review date, and planned resolution.
4. Validate the operational process
Test blocking in a controlled environment following Microsoft’s guidance. Have the responsible owners exercise the tasks that depend on the affected storage, using acceptance criteria agreed in advance. Retain the results and resolve any failures before closing the work.
5. Track the findings through to closure
Keep a shared record of affected dependencies, owners, actions, validation results, and exceptions. Use the existing change process where it provides sufficient control, and add coordination where dependencies cross teams. Close each finding when remediation and validation are complete.
From one deadline to continuous change management
This deadline also provides a useful opportunity to review how the organization handles security changes with deferred enforcement. A consistent process can connect technical findings to accountable owners, scheduled actions, and evidence of acceptance. Teams can reuse that process as subsequent changes arrive, with the level of effort scaled to each assessment.
The value builds across successive changes. A shared view of ownership, outstanding work, and exceptions helps teams manage overlapping deadlines and gives leaders evidence of readiness. Establishing those practices during a focused assessment creates a foundation for continuous change management.
How Juriba DPC can help
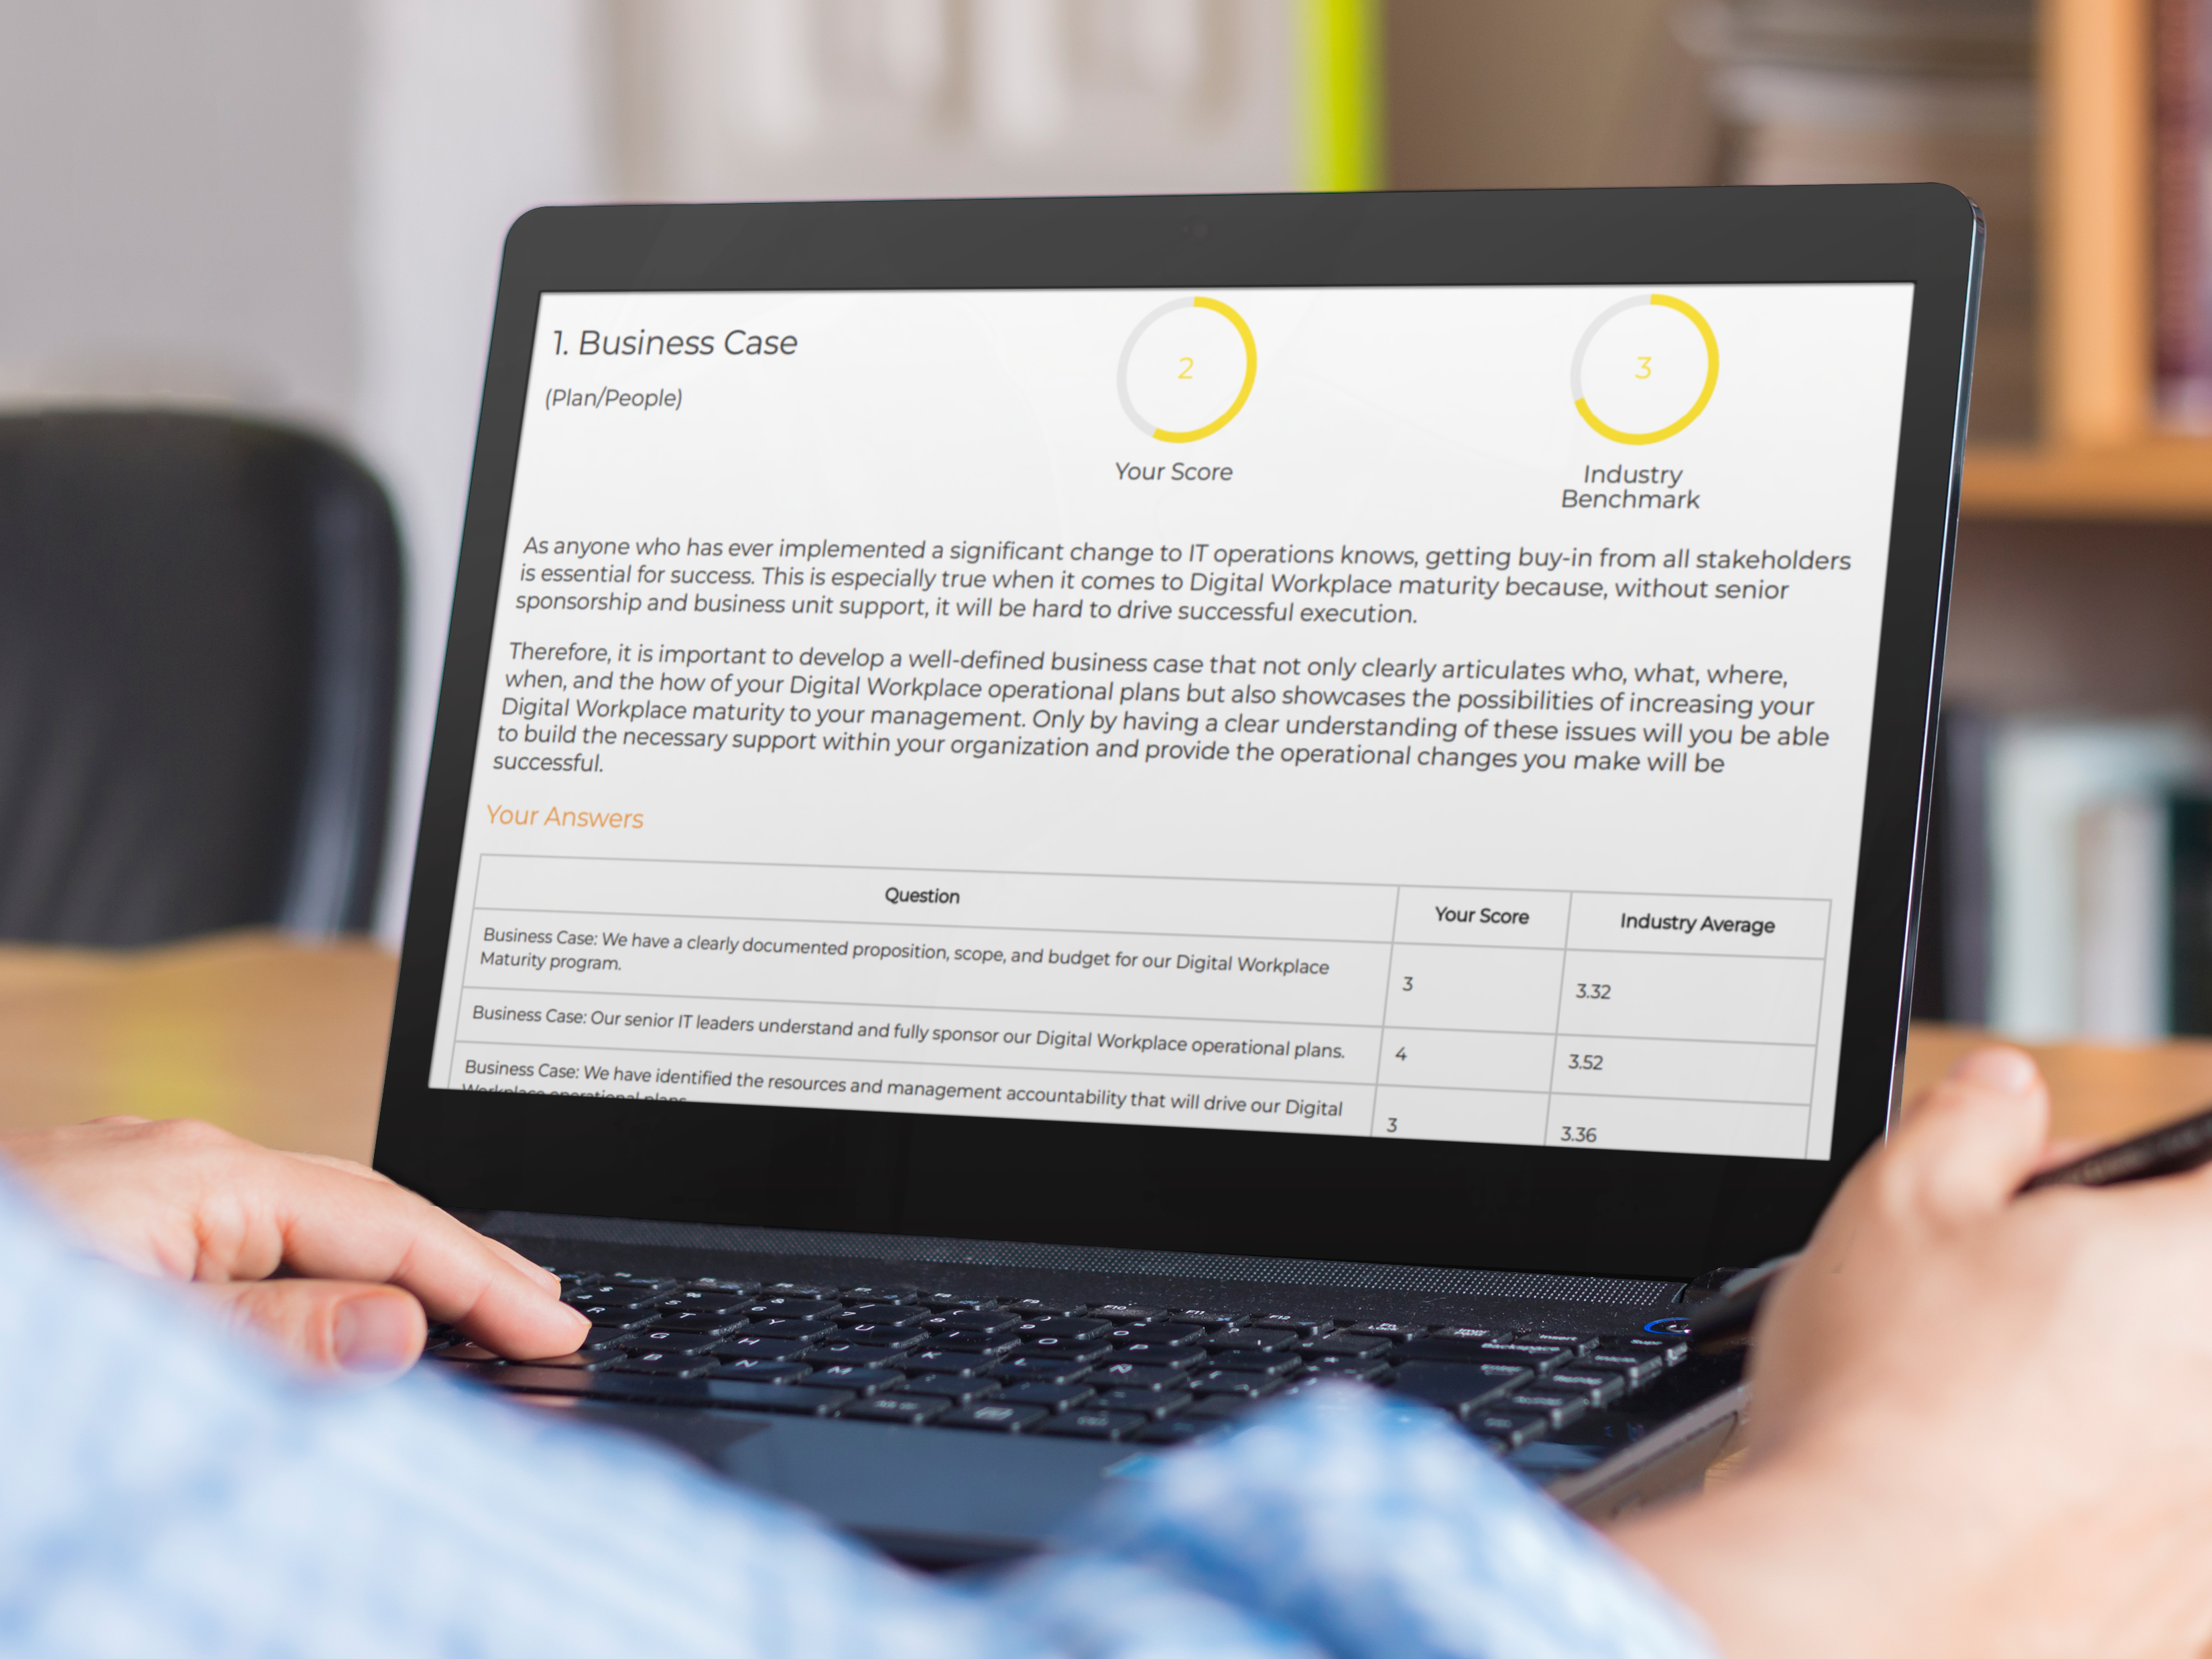
Juriba DPC can help organizations build a repeatable approach to change through configurable workflows, readiness tracking, targeted communications, and progress dashboards. For changes such as Microsoft’s ReFS enforcement, these capabilities can help teams coordinate assessments, assign ownership, and track remediation through validation. The same approach supports ongoing change across applications, devices, and infrastructure, giving teams a consistent way to manage future deadlines.